Buy wohnung-mieten.eu ?
We are moving the project
wohnung-mieten.eu .
Are you interested in purchasing the domain
wohnung-mieten.eu ?
domain@kv-gmbh.de · 0541-91531010
Buy wohnung-mieten.eu ?
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **


Similar search terms for Tpm
Top-Angebote
Products related to Tpm:
-
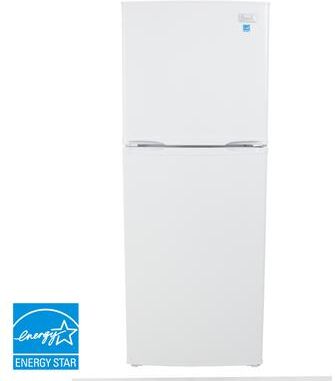
Avanti 11.6 cu. ft. Apartment Size Refrigerator, in WhiteStore your favorite food and beverages in this 11.6 cubic feet, white refrigerator from Avanti. The perfect apartment-size refrigerator, your food, and beverages stay fresh and cold thanks to the frost-free defrost system.965,99 $*Shipping: 0,00 $Secure redirect to the provider
-
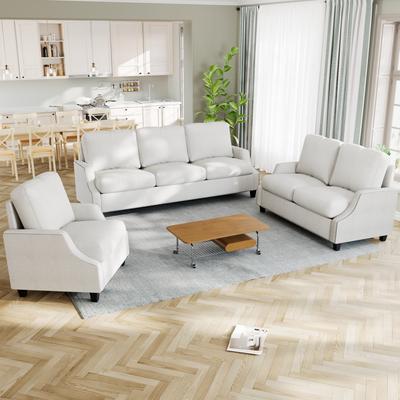
GDFStudio - Polyester 3-Piece Living Room Sofa Furniture Sets for ApartmentStatement Scale & Balanced Proportion: This three-piece living room set is designed to form an inviting yet composed seating group for everyday life — a three-seater sofa, a two-seater loveseat and a single accent chair that together offer abundant…937,38 $*Shipping: 0,00 $Secure redirect to the provider
-
Space-Saving Foldable Computer Desk for Home Office, Bedroom, Dorm, Apartment"This foldable desk offers a wide surface for laptops, monitors, or decor, along with shelves and storage for books and supplies. Its space-saving design folds down to just 13.14"" wide, making it ideal for bedrooms, apartments, dorms, and small offices."445,49 $*Shipping: 0,00 $Secure redirect to the provider


-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
-
Does it support TPM 2.0?
Yes, the device supports TPM 2.0. TPM (Trusted Platform Module) 2.0 is a security feature that provides hardware-based security functions, such as cryptographic keys and secure boot, to help protect the device from unauthorized access and tampering. This ensures that the device has a secure foundation for running trusted applications and protecting sensitive data. **
-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
Which one fits with TPM 20?
TPM 2.0 (Trusted Platform Module 2.0) is a hardware-based security solution that is designed to provide a secure foundation for various computing devices. It is typically integrated into the motherboard of a device and provides features such as secure boot, cryptographic key generation and storage, and hardware-based device authentication. TPM 2.0 is designed to enhance the security of devices and protect against various types of attacks, making it a suitable choice for organizations and individuals looking to secure their computing infrastructure. **
Top-Angebote
Products related to Tpm:
-
Stellar Zero Uncoated Apartment Essentials BundleEnjoy effortless cooking without traditional non-stick coatings with the Stellar Zero Uncoated Apartment Essentials Bundle. Made from 100% pure stainless steel with an innovative precision-etched cooking surface, this versatile three-piece set provides excellent food release without the use of PFAS or PTFE coatings. Featuring Tri-Ply construction, each pan combines layers of stainless steel and aluminium to provide fast, even heat distribution and excellent temperature control. The pans respond quickly to changes in heat, helping you achieve consistent results while cooking efficiently. The set includes a 24cm frying pan, 28cm sauté pan with glass lid and a 24cm casserole, providing three essential pieces for everyday cooking. From frying and searing to simmering, slow cooking and preparing family favourites, this versatile selection is ideal for a wide range of dishes. The uncoated stainless steel construction offers the durability of stainless steel without a conventional non-stick coating. The precision-etched surface is designed to provide non-stick performance and is safe to use with metal utensils, making it well suited to everyday cooking. Suitable for all hob types, including induction, the cookware is oven safe up to 240°C and dishwasher safe for easy cleaning. Backed by Stellar's 25-year guarantee, the Zero collection combines innovative uncoated cooking technology with durable construction designed to last.224,95 £*Shipping: 0,00 £Secure redirect to the provider
-
Avanti 11.6 cu. ft. Apartment Size Refrigerator, in WhiteStore your favorite food and beverages in this 11.6 cubic feet, white refrigerator from Avanti. The perfect apartment-size refrigerator, your food, and beverages stay fresh and cold thanks to the frost-free defrost system.965,99 $*Shipping: 0,00 $Secure redirect to the provider
-
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
-
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **
-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
Similar search terms for Tpm
-
GDFStudio - Polyester 3-Piece Living Room Sofa Furniture Sets for ApartmentStatement Scale & Balanced Proportion: This three-piece living room set is designed to form an inviting yet composed seating group for everyday life — a three-seater sofa, a two-seater loveseat and a single accent chair that together offer abundant…937,38 $*Shipping: 0,00 $Secure redirect to the provider
-
Space-Saving Foldable Computer Desk for Home Office, Bedroom, Dorm, Apartment"This foldable desk offers a wide surface for laptops, monitors, or decor, along with shelves and storage for books and supplies. Its space-saving design folds down to just 13.14"" wide, making it ideal for bedrooms, apartments, dorms, and small offices."445,49 $*Shipping: 0,00 $Secure redirect to the provider
-
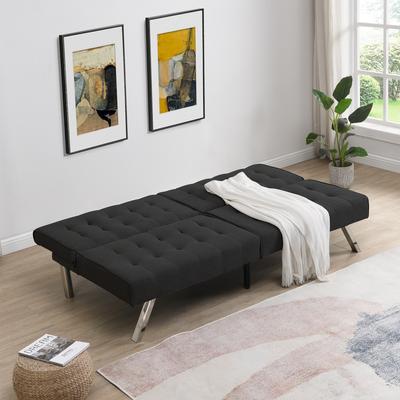
Modern Couch Fabric Comfy Sofa bed for Apartment, Living Room, StudioProduct Features Multifunctional sofa bed:Suitable for Any Scene,No Longer Worry about Unexpected Guests. User-friendly Design: easy to store the chair and save space for unused time.289,99 $*Shipping: 0,00 $Secure redirect to the provider
-
Does it support TPM 2.0?
Yes, the device supports TPM 2.0. TPM (Trusted Platform Module) 2.0 is a security feature that provides hardware-based security functions, such as cryptographic keys and secure boot, to help protect the device from unauthorized access and tampering. This ensures that the device has a secure foundation for running trusted applications and protecting sensitive data. **
-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
-
How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
-
Which one fits with TPM 20?
TPM 2.0 (Trusted Platform Module 2.0) is a hardware-based security solution that is designed to provide a secure foundation for various computing devices. It is typically integrated into the motherboard of a device and provides features such as secure boot, cryptographic key generation and storage, and hardware-based device authentication. TPM 2.0 is designed to enhance the security of devices and protect against various types of attacks, making it a suitable choice for organizations and individuals looking to secure their computing infrastructure. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.